Proof launches x401: verified legal identity and signed authorization for AI agents
Proof put the first production-grade identity layer for the agentic web into production today: x401, an open protocol that lets any website ask an AI agent to prove who it's acting for — and produce a cryptographically signed receipt of exactly what that person approved. Meta's Muse, ChatGPT dots, Grok, and Claude work with it through a production MCP server.
Today, identity infrastructure company Proof put verified legal identity and transaction authorization for AI agents into production with the launch of x401 — an open protocol that lets any website ask an AI agent two questions its predecessors could never answer reliably: who are you acting for, and can you prove that person authorized this exact action?
At the center is an agent identity wallet held by the consumer. The wallet stores a verified legal identity and lets the person approve, on their own device, exactly what their agent may do. The agent carries the request; the person's wallet signs it. The receiving business can independently confirm the consumer's verified identity and check the cryptographic signature on the transaction itself — and if the agent alters the amount, recipient, or any other signed term, the signature no longer validates. Independent coverage from GenZ NewZ describes it as the first production deployment of verified legal identity for the agentic web.
Three capabilities are live today: the agent identity wallet, the x401 open HTTP protocol itself, and a production Model Context Protocol (MCP) server that works with Meta's Muse, ChatGPT dots, Grok, and Claude.
Why now: the week Amazon blocked an agent
On September 8, Meta released Muse, an AI agent capable of completing purchases. It reached No. 1 on the U.S. App Store, and Shopify connected Shop Pay. On September 21, Amazon blocked Muse from its marketplace, saying the agent did not identify itself, appeared to collect customer credentials, and moved through accounts and transactions without Amazon's knowledge or consent.
Proof calls the underlying problem the "Agent Evidentiary Gap": the distance between what an AI agent can technically do and what a business can verify the person behind it authorized. An agent may hold a valid password, OAuth token, API key, or payment card — none of that establishes that the person authorized a particular action. Consumers are wary too: in a survey of 1,000 U.S. consumers by Exploding Topics, 31% said they would not let an AI agent spend any money on its own, and 51% were uncomfortable with AI tools storing their card details.
How x401 works: verify the person, sign the action
x401 extends HTTP 401, the web's standard unauthorized-response mechanism, so a website can specify the evidence an AI agent must provide before proceeding. A site can request verified identity claims — legal name, age, or nationality — from trusted issuers at a required level of assurance, and can require the consumer to cryptographically sign the terms of a specific transaction.
The flow: the agent presents the request to the consumer, who authenticates with a biometric on their own device. Proof's wallet shows the information and transaction terms being requested; on approval, a hardware-protected key signs the presentation, binding the verified legal identity to the specific terms. The website then verifies the issuer, credential, signature, and transaction terms before proceeding — and can retain the signed evidence to validate independently if the transaction is ever disputed.
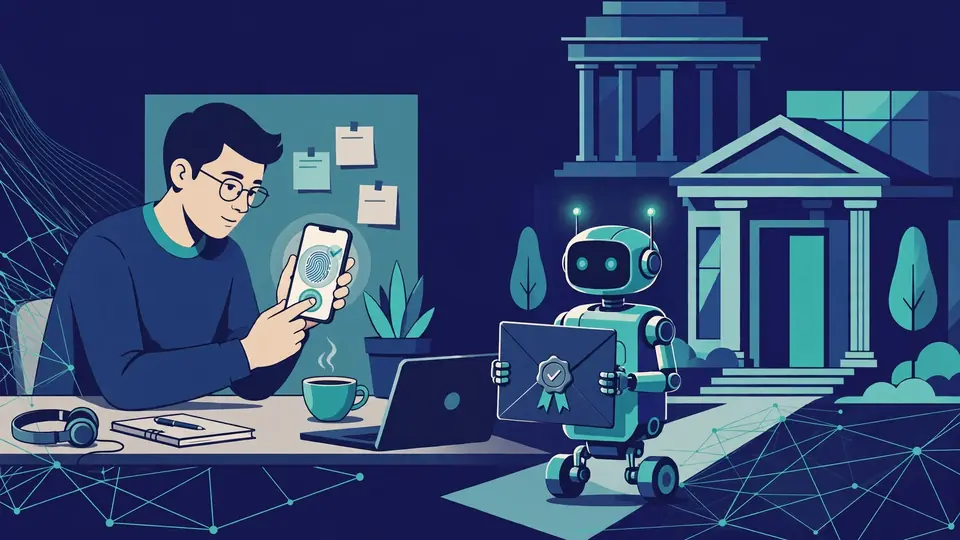
The canonical example from the launch: an agent instructed to transfer $25,000 from a consumer's bank account. The bank issues an x401 challenge requiring verified legal identity plus a signature on the wire instructions — amount, recipient, source account. The consumer reviews and approves on their own device; the bank verifies the signed instructions alongside its own requirements before executing. If any signed detail changes, the evidence fails verification.
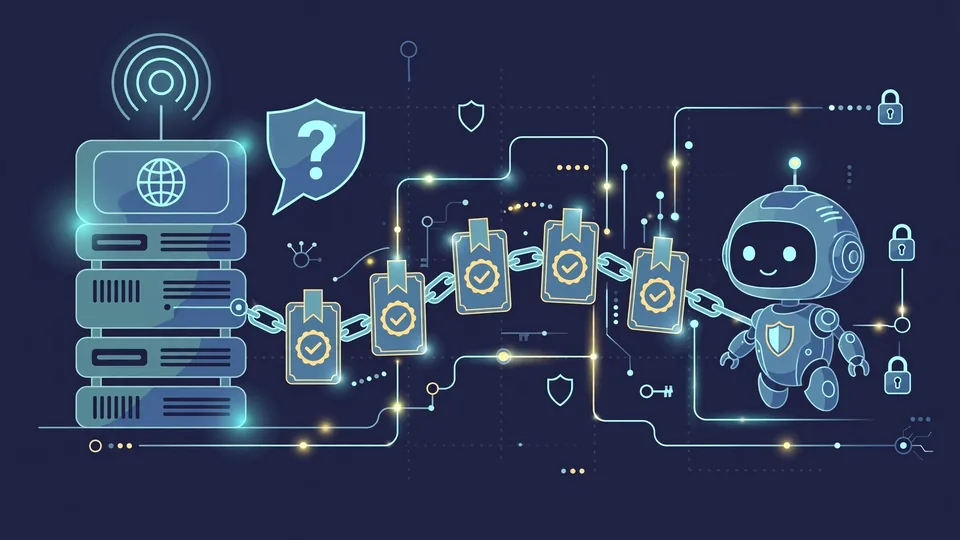
x401 meets x402: identity and payment as open plumbing
Proof designed x401 to work alongside x402, the HTTP-native payment protocol now stewarded by the Linux Foundation, which had more than 40 member organizations as of July 2026, including Visa, Mastercard, Stripe, Google, AWS, Circle, and Coinbase. The division of labor: x401 establishes who is behind a request and can carry cryptographically signed evidence of what they approved; x402 moves the payment.
Proof is also using x402 to change the economics of identity verification itself. Historically, selling a verification that costs cents required enterprise agreements, because collecting the payment wasn't practical. With x402, a website can pay Proof per claim — no purchase order, no invoice, no minimum commitment — so identity can be metered like bandwidth or compute: one API request, one agent purchase, one machine-signed document at a time.
The legal layer: credentials that hold up in a dispute
Each verified person holds an X.509 certificate issued by Proof's WebTrust-audited certificate authority, following Kantara-certified NIST IAL2 identity proofing, bound to a hardware-protected key. The credential belongs to the person, not an institution, and can be reused across relationships. Selective disclosure lets consumers share specific attributes without exposing an entire identity document.
The timing isn't accidental. On September 8, FinCEN — together with staff from the Federal Reserve, FDIC, NCUA, and OCC — updated Customer Identification Program guidance to expressly recognize digital certificates and verifiable credentials, including those issued by nongovernment third parties, as permissible customer-identity verification methods. And x401 is designed to interoperate with AP2 and Verifiable Intent, the specifications developed by Google and Mastercard and now stewarded by the FIDO Alliance, for recording what a person authorized an agent to do.
Already in production
This isn't a white paper. Superfluid, which operates settlement infrastructure for tokenized markets, announced in September the first live implementation of x401 with Proof as part of its wallet launch. Proof has published the full protocol and identity scheme at proof.com/x401 — credential formats, issuance, custody, presentation, transaction signing, agent delegation, settlement, claims, offline verification, and implementation guides — and says it intends to place the protocol under neutral, independent governance.
Developers can deploy today through a reference implementation for Cloudflare Workers, with guides for Node, Python, Go, and other environments; basic identity claims — verified age, country of residence, email — can be requested with no sales process or negotiated agreement. Proof will demonstrate the end-to-end experience at Money20/20 in Las Vegas, October 18–21, at Booth #5069.
Proof itself is no stranger to high-stakes identity: it operates identity infrastructure across mortgage, automotive, wealth, insurance, and enterprise markets, runs a network of more than 8,000 businesses, says more than $1 trillion in transactions has been secured on its platform, created the online notarization category, and operates the Notarize Network.
Practical knobs: --limit caps results (default 7), --preview none|short|full controls how much context each hit shows, and --human forces the readable layout when output is piped.
Step 5 — Keep the index honest #
An index is only useful if you can trust its freshness. zg exposes that explicitly instead of hiding it:
# Default: background refresh (file events + interval sweeps)
zg query "retry backoff"

# Reindex changed files first, then answer
zg query "retry backoff" --refresh wait

# Answer from the index as-is, even if files changed
zg query "retry backoff" --refresh off
Hits carry a freshness marker, so --refresh off will tell you a result is possibly_stale rather than silently serving it. When the index needs surgery: zg index --rebuild rebuilds it in place, and zg index --drop --yes removes it entirely. This explicitness is a design choice worth appreciating — most "smart search" tools either reindex opaquely or go stale quietly; zg does neither.
Step 6 — Hand it to your agent #
Semantic code search is arguably more valuable to agents than to humans — an agent exploring a new repo asks "where is X handled?" constantly, and burning context on blind grep sweeps is expensive. zg ships a first-class MCP path:
# Wire zg into your coding agent (codex, claude, qwen, qoder,
# opencode, cursor, copilot, vscode, all, or auto)
zg install --target claude

# Or run the daemon yourself: stdio for agents, HTTP for tools
zg server on
# Server: ready
# URL: http://127.0.0.1:7999/mcp
zg server status
zg server off
Two details matter. The MCP endpoint binds to loopback only (127.0.0.1) — your index never leaves the machine, which is the whole point of the local-first design. And the default agent toolset exposes exactly one tool, zvec_grep_search, keeping the agent's tool surface minimal; --mcp-toolset full adds rg, index, index_drop, index_status, and server_status for operators who want them.
The project's own guidance is refreshingly honest about the division of labor: use semantic search for meaning, but keep native grep/ripgrep for exact identifiers, paths, and regex. The --rg route exists precisely so the agent doesn't have to shell out to a second tool.
zg vs the alternatives #
| Tool | Strength | Where zg wins |
|---|---|---|
| ripgrep | Instant, exact, zero setup | When you don't know the words; zg keeps rg inside it anyway |
| GitHub code search | Symbol-aware, huge index | Local, private, works on unpushed code, no cloud round-trip |
| Sourcegraph / Cody | Full platform, cross-repo | One npm install, no account, no per-seat anything |
| DIY vector RAG | Fully customizable | No chunking/embedding plumbing; BM25+vectors+rg pre-fused |
The honest summary: zg doesn't replace ripgrep — it absorbs it and adds the two things rg can't do (ranked keywords, meaning). Its real competitors are the hosted code-intelligence platforms, and its pitch against them is radical simplicity: one CLI, one local index, no bill.
Limitations worth knowing #
No tutorial is complete without the rough edges — all observed or documented, none guessed:
- Pre-1.0 API churn is real. The online docs already describe a newer flag form than the 0.2.2 you install from npm today. Pin your version, and trust
zg --helpover blog posts (including this one, in six months). - Semantic search costs latency. One published independent evaluation measured roughly 0.9 s per semantic query versus 0.01 s for ripgrep, and found semantic hits skew toward explanatory prose (READMEs, comments) over production code. Use
--rgwhen milliseconds matter. - Some formats are skipped by design — PDFs, Office documents, archives, executables, media files, and databases never enter the index. If your answers live in a Confluence export, zg won't see them.
- Remote embeddings are gated. Cloud models (OpenAI, Qwen, custom endpoints) require explicit opt-in flags and your own API key — local is the default and the path this tutorial tested.
- Benchmarks are vendor-reported. The project cites SWE-QA-Bench (with Claude Code + Opus 5) and BrowseComp-Plus (with Codex + GPT-5.6-class models) plus case studies on pylint, matplotlib, and Django. Treat those as the project's claims, not independent verification — the one independent evaluation linked below is more mixed, which is normal for a three-month-old tool.
The takeaway #
The reason zvec-grep is trending isn't a benchmark number — it's that the workflow finally matches how developers actually think. You describe the behavior; it finds the code. The hybrid default means you rarely have to care which engine answered, the managed ripgrep means you never lose exact search, and the MCP server means your agent gets the same superpower with one install command. For the price of npm install -g @zvec/zvec-grep and ~160 MB of one-time model downloads, "where is the session logic?" becomes an answered question instead of a twenty-minute spelunk.
Index one of your own repos tonight. Run zg status, then ask it the question you'd normally grep for — phrased the way you'd explain it to a new teammate. If the top hit is right, you'll understand the 3,800 stars.